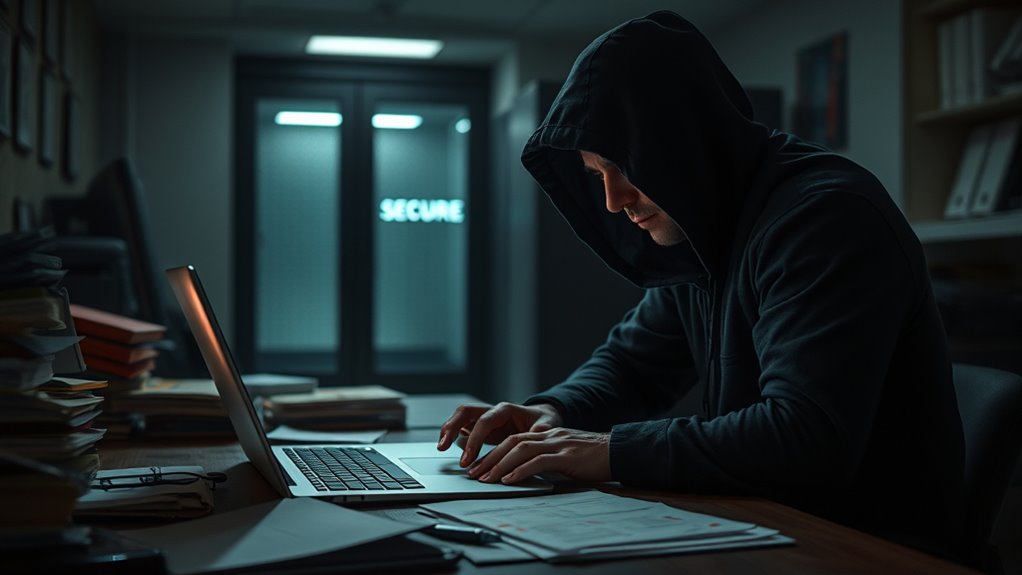
A single insider with malicious intent or carelessness can severely harm national security by exploiting trusted access to essential information and systems. They can cause data breaches, operational disruptions, or security failures that large external attacks might take years to create. Your awareness and vigilance are critical; recognizing suspicious behaviors and fostering a security-first environment helps prevent these threats. Keep exploring to understand how insider traits can be managed to protect your organization and nation.
Open a free Amazon Business account
Business pricing, bulk buying and tax-exempt orders.
As an affiliate, we earn on qualifying purchases.
Key Takeaways
- A single insider with malicious intent can access and leak sensitive national security information, causing severe damage.
- Insider threats often go unnoticed until their actions result in data breaches or operational disruptions.
- Lack of vigilance and weak cybersecurity protocols increase the risk of insiders compromising national security.
- Cultivating a security-first culture and employee awareness can help detect and prevent insider threats.
- Strict access controls, monitoring, and regular audits are essential to minimize the impact of insider betrayal.
Have you ever considered how much damage an insider threat can cause? It’s a danger that’s often underestimated until it’s too late. When someone inside your organization turns malicious or careless, the consequences can be devastating, especially regarding national security. The key to preventing such threats lies in maintaining high employee vigilance and strictly adhering to cybersecurity protocols. You need to understand that insiders have unique access and knowledge, making their actions potentially more harmful than external attacks.
Employee vigilance isn’t just about watching for suspicious behavior; it’s about fostering a culture where security is everyone’s responsibility. When you stay alert to unusual activities—such as unauthorized data access, repeated login failures, or sudden changes in work patterns—you catch potential threats early. Training your staff to recognize signs of insider risks makes a significant difference. It’s essential that employees know what behaviors to report and feel empowered to do so without fear of reprisal. This proactive approach creates a security-minded environment where threats are identified before they escalate. Promoting cybersecurity awareness helps embed these practices into daily routines.
Fostering a security culture empowers employees to identify and report insider risks early.
Cybersecurity protocols serve as the backbone of your defense against insider threats. These protocols define how sensitive information is stored, accessed, and monitored. Regular updates and audits are vital because cyber threats evolve constantly. You should enforce strict access controls, ensuring that employees only see what’s necessary for their roles. Multi-factor authentication adds an extra layer of security, making it harder for malicious insiders to exploit their privileges. Encryption, activity logging, and real-time monitoring further strengthen your defenses.
However, protocols alone aren’t enough. You must cultivate a security-first mindset within your organization. This means continuous training sessions that reinforce best practices, such as creating strong passwords and recognizing phishing attempts. When employees understand the importance of cybersecurity, they become active participants in preventing insider threats. This proactive stance diminishes the likelihood of careless mistakes or malicious actions slipping through.
multi-factor authentication security device
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Frequently Asked Questions
How Are Insider Threats Detected Early?
You can detect insider threats early by monitoring behavioral indicators and access anomalies. Pay attention to unusual activity, like sudden data downloads or accessing restricted areas without cause. Use advanced security tools to flag these irregularities and conduct timely investigations. Training staff to recognize warning signs also helps. By staying vigilant and employing proactive detection methods, you increase your chances of catching threats before they cause significant harm.
What Legal Consequences Do Insider Threats Face?
Like a shadow lurking in the dark, insider threats face serious legal ramifications. You could be criminally prosecuted, facing fines, imprisonment, or both, depending on the severity of your actions. These legal consequences serve as a stern warning that betrayal doesn’t go unpunished. Authorities take insider threats seriously, ensuring that traitors pay a heavy price for compromising national security, deterring others from walking the same treacherous path.
How Can Organizations Prevent Insider Threats?
You can prevent insider threats by implementing employee monitoring to detect suspicious behavior early. Foster a strong culture of awareness by educating staff about security risks and ethical standards. Regularly review access controls, enforce strict policies, and encourage open communication. Building trust and vigilance helps you identify potential threats before they cause harm, safeguarding your organization’s sensitive information and maintaining overall security.
Are Insider Threats More Common in Specific Industries?
Ever wondered which industries face the highest insider threat risks? You should know that insider threats are more common in sectors with industry-specific vulnerabilities and sector risk factors, like defense, finance, and healthcare. These industries handle sensitive data and assets, making them prime targets for malicious insiders. Your organization must stay vigilant by understanding these sector-specific risks and implementing tailored security measures to prevent insider threats effectively.
What Psychological Traits Are Common Among Insider Threats?
You should know that insider threats often share personality vulnerabilities like impulsiveness or resentment, which make them susceptible to manipulation. Motivational factors such as financial hardship, grievances, or ideological beliefs can push someone toward betrayal. Recognizing these traits helps you identify potential risks early. By understanding their psychological vulnerabilities and motivations, you can implement better security measures and foster a supportive environment that reduces the likelihood of insider threats.
Conclusion
Remember, even the most trusted allies can sometimes drift from the path of loyalty. By staying vigilant and fostering strong bonds, you can help safeguard your organization’s future. A single misstep, though subtle, can cast long shadows. Embrace awareness and caution, ensuring that the light of integrity always guides your way. In doing so, you protect not just your work but the greater good, turning potential vulnerabilities into pillars of strength.
NFL season / tailgating Picks
team gear
As an affiliate, we earn on qualifying purchases.