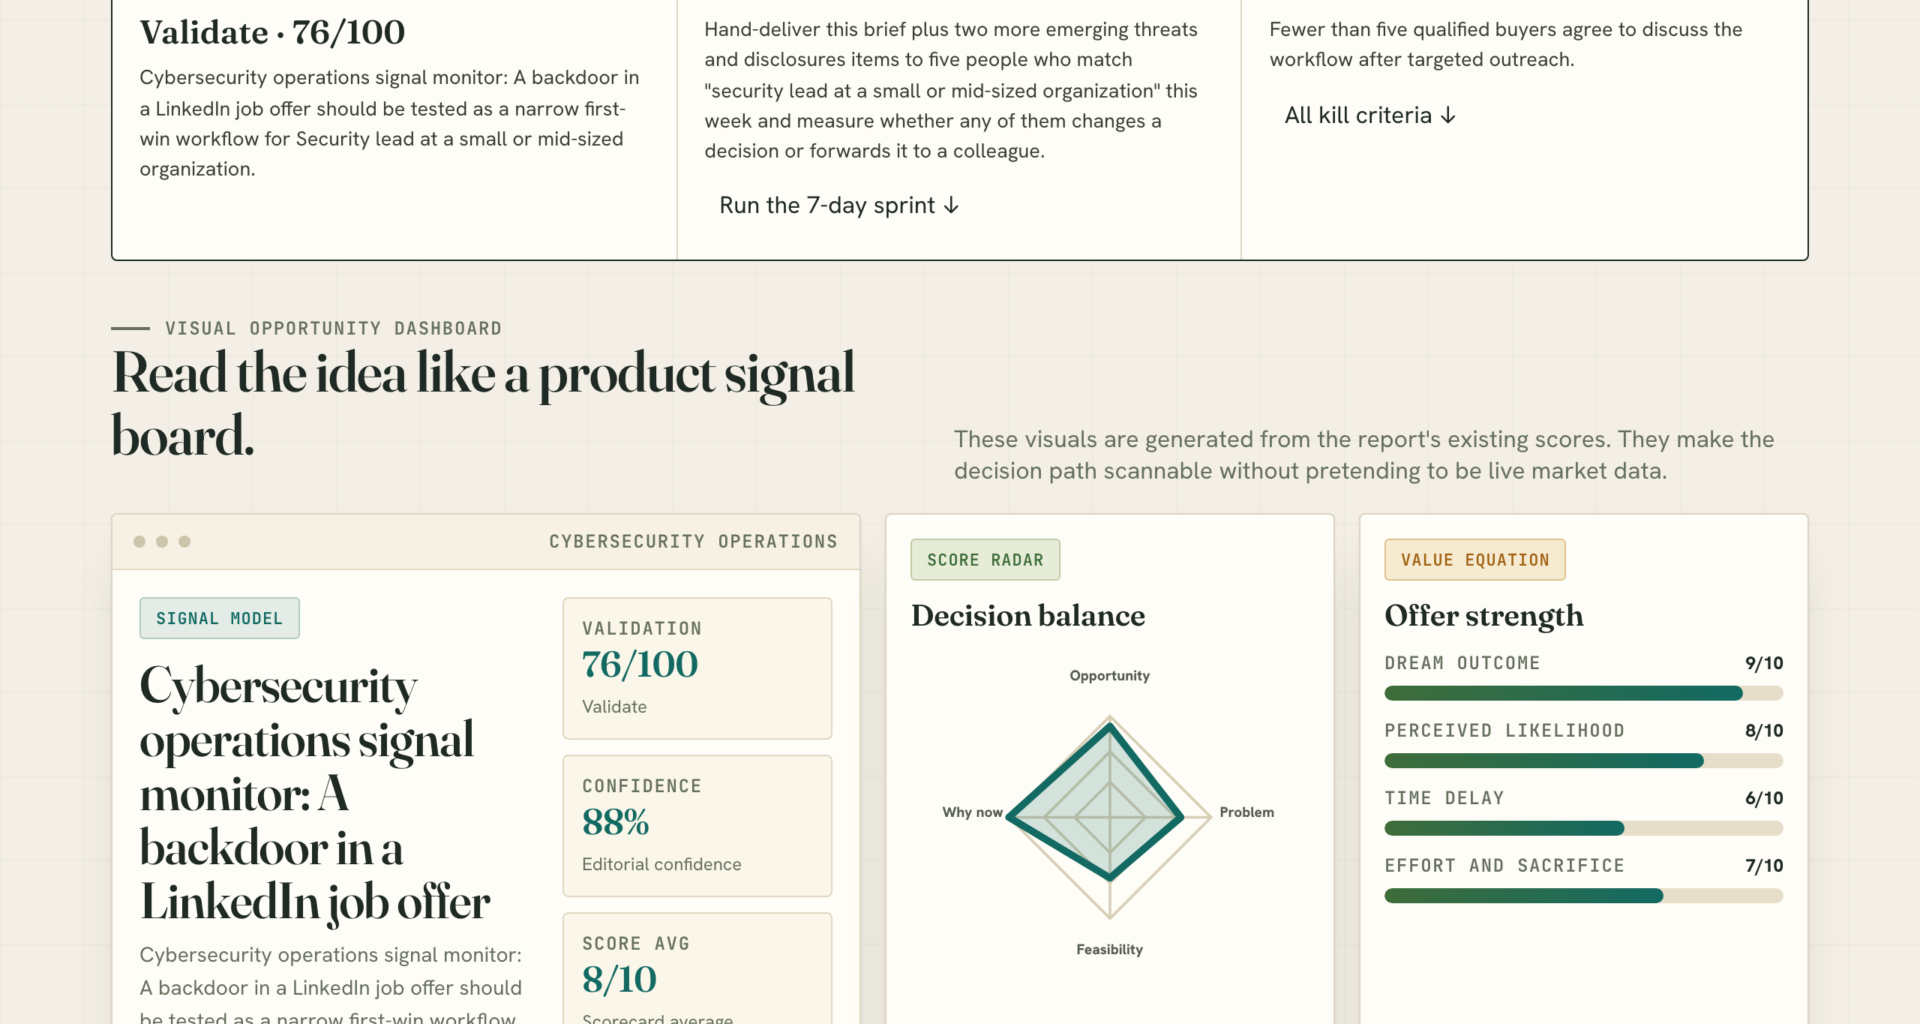
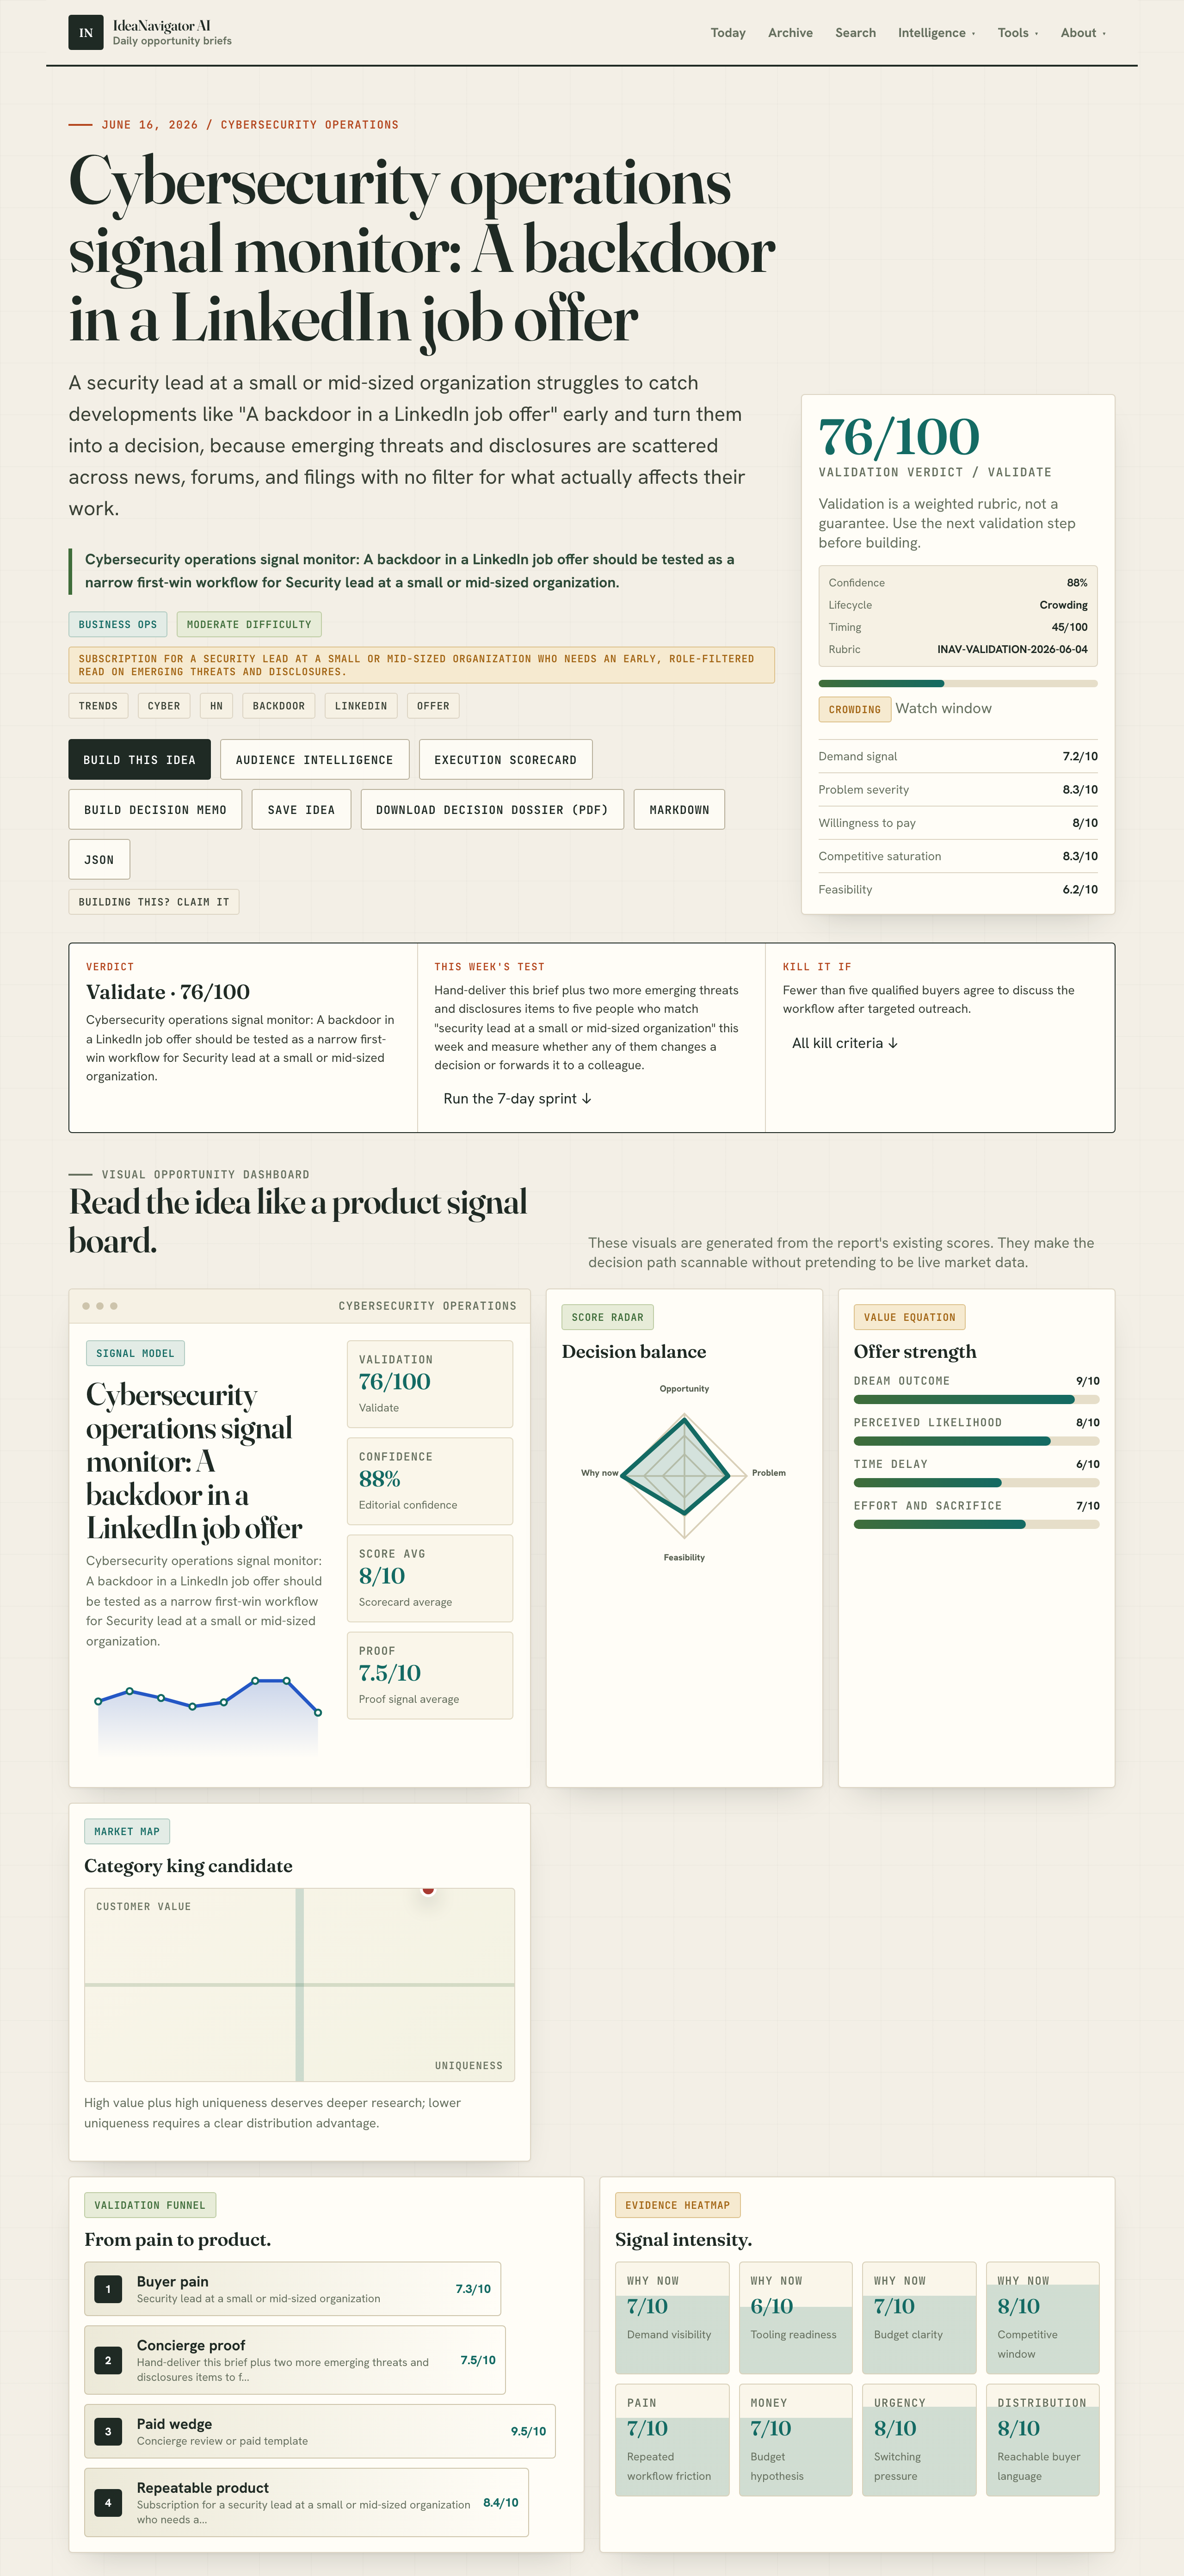
📊 Full opportunity report: Cybersecurity Operations Alert: Detecting Backdoors In LinkedIn Job Listings on IdeaNavigator AI — validation score, market gap, and execution plan.

Get privacy and security gear delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
TL;DR
Cybersecurity operations have detected indications of backdoor vulnerabilities in LinkedIn job listings. This development signals new risks for organizations using online hiring platforms. The findings are preliminary but prompt urgent review of recruitment-related cybersecurity measures.
Cybersecurity analysts have identified potential backdoor vulnerabilities embedded within some LinkedIn job listings, marking a new development in online threat activity. This discovery is significant for organizations relying on LinkedIn for recruitment, as it suggests a possible avenue for cyberattackers to compromise corporate networks. The alert underscores the importance of scrutinizing recruitment channels for security risks.
Recent signals from cybersecurity operations indicate that certain LinkedIn job postings may contain malicious backdoors designed to facilitate unauthorized access. The detection was triggered by monitoring emerging threats on platforms like Hacker News, which assigned an 88/100 signal score to this particular threat. Experts warn that such backdoors could be exploited by hackers to deploy malware, steal data, or gain persistent access to organizational systems.
While the specific technical details of the backdoor mechanisms are still under investigation, cybersecurity professionals emphasize the importance of heightened vigilance. Organizations are advised to review their recruitment processes, verify the authenticity of job postings, and implement additional security checks on external links and attachments associated with online applications. No confirmed breaches have yet been reported, but the potential risk has prompted immediate alerts from security teams.
Potential Impact of Backdoors in Recruitment Platforms
This development matters because it exposes a new attack surface for cybercriminals targeting organizations through their hiring channels. As LinkedIn is widely used for recruitment, malicious actors could leverage compromised postings to infiltrate corporate networks, leading to data breaches or operational disruptions. Early detection and response are critical to prevent exploitation, especially given the speed at which such threats can propagate.
cybersecurity threat detection tools
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Emerging Threats in Online Recruitment Platforms
Over the past year, cyber threats have increasingly targeted online platforms used for business functions, including recruitment. Prior incidents involved phishing scams and malicious links, but the recent identification of backdoors in LinkedIn job listings marks a shift toward more sophisticated, embedded exploits. This aligns with broader trends of cybercriminals embedding malicious code in seemingly legitimate online content to evade detection.
The alert was prompted by a cybersecurity signal monitoring system that filters emerging threats from sources like Hacker News. The threat received a high signal score, indicating a notable level of concern among security professionals. The investigation is ongoing, and details about the specific backdoor exploits remain classified pending further analysis.
Unconfirmed Technical Details and Extent of Exploits
It remains unclear how widespread the backdoor embedding is across LinkedIn job listings, and whether any organizations have already been compromised. The technical specifics of the backdoor mechanisms are still under investigation, and no confirmed breaches have been publicly reported. The full scope and potential impact of these exploits are not yet known.
Ongoing Investigations and Recommended Security Measures
Security teams are actively analyzing the affected postings and developing detection tools to identify malicious backdoors. Organizations are advised to conduct thorough reviews of their recruitment processes, verify the legitimacy of job postings, and implement enhanced security measures such as link scanning and attachment verification. Further updates are expected as investigations progress and more technical details become available.
Key Questions
What are backdoors in LinkedIn job listings?
Backdoors in LinkedIn job listings refer to malicious code or links embedded within postings that could allow hackers to gain unauthorized access to organizational networks.
How can organizations protect themselves from this threat?
Organizations should verify the authenticity of job postings, scrutinize external links, monitor for unusual activity, and update security protocols related to online recruitment channels.
Has any organization been compromised so far?
There are no publicly confirmed reports of breaches resulting from these backdoors at this time. The threat is still under investigation.
What should security teams do right now?
Security teams should review current recruitment processes, implement additional verification steps, and stay updated on ongoing investigations and technical findings.
Will this affect all LinkedIn job listings?
It is not yet clear how widespread the issue is. Ongoing investigations aim to determine the scope of affected postings.
Source: IdeaNavigator AI
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.