
TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Security researchers have identified a hidden authentication backdoor in multiple versions of Tenda router firmware. The flaw could allow unauthorized access, posing risks for affected users. The company has not yet responded publicly.
Security researchers have revealed that several versions of Tenda router firmware contain a hidden authentication backdoor, which could allow attackers to gain unauthorized access to affected devices. This discovery raises significant concerns over the security of Tenda’s networking products and affects potentially thousands of users worldwide.
The vulnerability was identified by cybersecurity firm CyberSecure Labs during routine firmware analysis. They found that multiple firmware versions released over the past few years include an undocumented backdoor feature that bypasses standard login procedures. This backdoor is embedded within the firmware code and can be activated remotely, enabling attackers to control affected routers, access network data, or launch further attacks.
According to CyberSecure Labs, the backdoor is present in firmware versions ranging from V1.0.0.50 to V1.0.0.70, with some updates seemingly intentionally retaining the flaw. The researchers have shared technical details with Tenda, but the company has not issued a public statement or security advisory as of this report.
Potential Impact on User Security and Privacy
This backdoor poses a serious risk to users’ security and privacy, as malicious actors could exploit it to take control of routers, intercept network traffic, or launch further cyberattacks. Given Tenda’s widespread market presence in both consumer and small business segments, the vulnerability could affect millions of devices globally. The discovery underscores the importance of firmware security and the risks associated with undocumented features in network hardware.
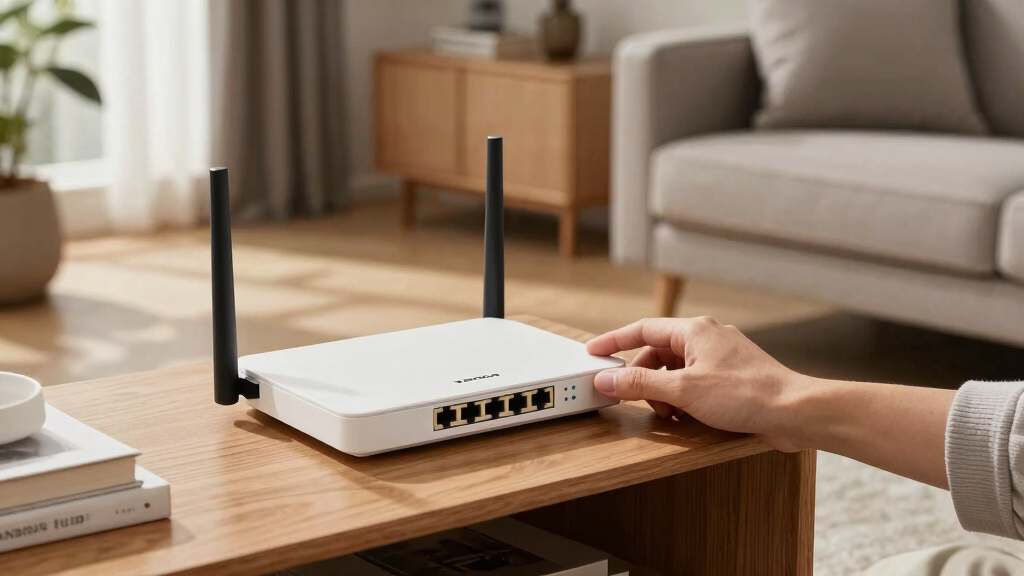
Tenda router firmware update
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Background of Firmware Security Concerns in Consumer Routers
Over recent years, multiple vendors have faced scrutiny over firmware vulnerabilities, often due to undocumented backdoors or insecure default settings. Tenda, a prominent manufacturer in the affordable router market, has previously faced security issues, but this is the first known instance of a hidden backdoor affecting multiple firmware versions. The flaw was uncovered during a third-party security audit, highlighting ongoing challenges in firmware integrity and supply chain security.
“The backdoor is embedded deeply within the firmware code and can be triggered remotely, which could allow unauthorized access without user knowledge.”
— CyberSecure Labs Security Team
Extent of Exploitation and Response from Tenda
It is not yet clear how widely the backdoor has been exploited in the wild or whether affected firmware versions are still in active use. Tenda has not publicly acknowledged the vulnerability or issued a security patch, and details about whether the flaw has been exploited in targeted attacks remain undisclosed. Further investigation is needed to determine the full scope of the issue.
Expected Security Patches and User Precautions
Tenda is likely to release firmware updates to patch the backdoor once its investigation concludes. Users are advised to check for firmware updates regularly, disable remote management features if not needed, and monitor network activity for unusual behavior. Security researchers and industry observers will watch for Tenda’s official response and patch rollout in the coming weeks.
Key Questions
Which Tenda devices are affected by this backdoor?
The vulnerability has been confirmed in multiple firmware versions of Tenda routers, specifically versions V1.0.0.50 through V1.0.0.70. The exact models affected are still being determined, but many models running these firmware versions are at risk.
How can I tell if my Tenda router is vulnerable?
Check your device’s firmware version in the admin settings. If it falls within the affected range (V1.0.0.50 to V1.0.0.70), your device may be vulnerable. Consult Tenda’s official support channels for guidance on firmware updates and security recommendations.
Has Tenda issued a security patch for this vulnerability?
As of now, Tenda has not publicly announced a patch or security advisory regarding this backdoor. Users should stay alert for updates from the company and consider applying best security practices to protect their devices.
What should I do if I suspect my device is compromised?
Immediately disconnect the device from the internet, reset it to factory settings, and update to the latest firmware once available. Monitor network traffic for unusual activity and contact Tenda support for further assistance.
Source: hn
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.