TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
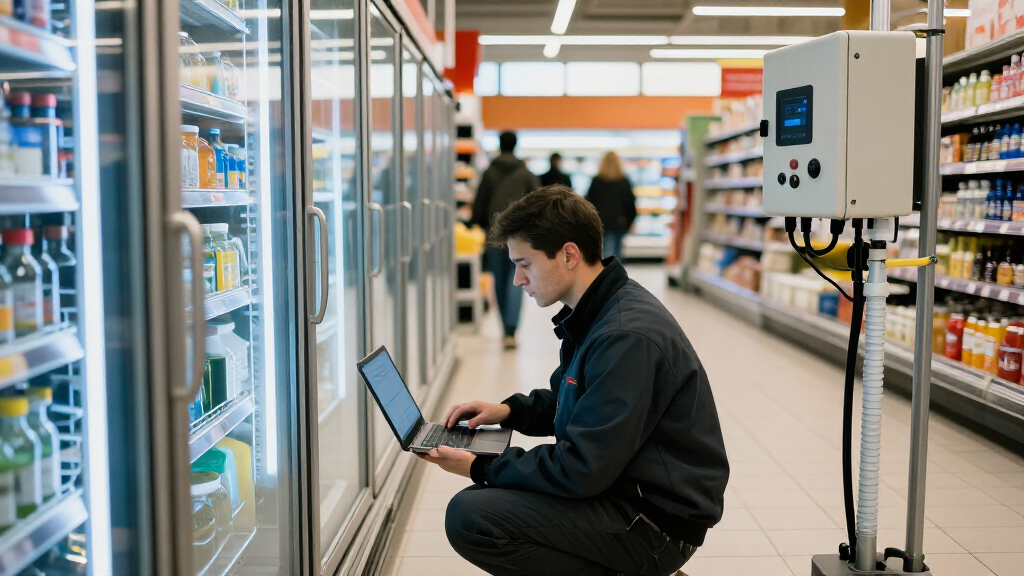
A cyberattack reportedly disrupted refrigeration controls at stores belonging to several French supermarket chains, including Intermarché, Leclerc and Coopérative U. Coopérative U’s president confirmed that refrigeration facilities in several stores were affected; the reported defrost settings and wider effects on deliveries and electronic prices have not been independently confirmed in the source material.
A reported cyberattack has affected refrigeration control systems at stores belonging to several French supermarket networks, with Coopérative U president Dominique Schelcher confirming that facilities in several stores were disrupted. The incident matters because failures in store refrigeration can threaten food storage and disrupt daily operations, although the reported settings, wider effects and overall scale have not been independently established in the available reporting.
Schelcher said refrigeration production facilities at several stores in the Coopérative U network had been affected since the previous night. He said teams had been mobilized to address the problem and that the retailer would investigate. He described the incident as “extremely serious,” but the source report did not provide a technical explanation of how the attack worked or identify those responsible.
Tom’s Hardware, citing French outlet La Dépêche, reported that Danfoss-made refrigeration controls used by Intermarché, Leclerc and Coopérative U were targeted. The article also reported that some units were set to continuously defrost at 50 degrees Celsius. That detail is attributed to the reporting, rather than confirmed in the quoted statement from Schelcher.
The same report said deliveries and electronic shelf-label pricing were also apparently affected. It did not specify which chains or stores experienced those problems, how many locations were involved, or whether refrigeration, delivery and pricing disruptions were linked to the same technical intrusion. No reported figures for spoiled goods, store closures or customer losses were provided.
Risks to Food Storage and Stores
Refrigeration is a core supermarket function: disruption can affect the safe storage of perishable products and require staff to check equipment and stock. If defrosting continues as described in the report, stores could face operational pressure while teams diagnose the controls and restore normal settings. The source material does not confirm that food was spoiled or that customers were exposed to unsafe products.
The reported effects on deliveries and electronic shelf labels, if confirmed, would broaden the incident beyond cooling equipment. Those systems support restocking and accurate display of prices, so problems could complicate store operations even where a location remains open. The evidence provided does not establish the scope of those effects or whether they occurred at the same sites as refrigeration failures.
The incident also underscores the importance of securing connected equipment used in essential retail operations. However, no information in the report establishes a vulnerability in Danfoss products, a compromise of the manufacturer itself, or a broader attack affecting supermarkets across Europe. The confirmed statement concerns several stores in Coopérative U’s network; the wider geographic wording remains a report-level characterization.
refrigeration control systems for supermarkets
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
What the Reports Establish
The initial account came from La Dépêche, as cited by Tom’s Hardware. It described several major retailers as targets and linked the affected refrigeration controls to equipment made by Danfoss. The material supplied for this article does not include a statement from Danfoss, the other named retailers, law enforcement or a national cybersecurity agency.
The clearest direct confirmation in the report is Schelcher’s statement about refrigeration facilities in several Coopérative U stores. He said the disruption began the previous night and that response teams were working on it. His remarks establish that the retailer acknowledged an incident; they do not independently verify the precise device settings, the suspected method of access, or the full list of affected businesses.
The report describes the incident as ongoing, but gives no calendar date for Schelcher’s Monday-morning comments. It also provides no confirmed count of stores, duration of outages or estimate of financial and product losses. Those gaps limit what can be concluded about the scale and duration of the event.
Scope and Cause Still Unconfirmed
The available reporting does not identify the attackers, explain how they gained access, or say whether a vulnerability or compromised account was involved. It is also unclear whether the alleged 50-degree-Celsius defrost setting was observed across multiple units or at particular locations. The quoted Coopérative U statement does not mention that setting.
The number of affected stores, the exact retailers and countries involved, and the duration of any disruption have not been specified. The reported effects on deliveries and electronic shelf labels remain insufficiently detailed. There is no information in the supplied material confirming food losses, safety incidents, customer data exposure, ransom demands, or a link to a wider campaign.
Retailers Investigate and Repair
Coopérative U said response teams had been mobilized and that the incident would be investigated. The next useful updates would establish whether affected controls have been restored, how many stores required intervention, and whether the reported delivery and pricing problems are verified. Confirmation from Intermarché, Leclerc, Danfoss or relevant authorities could clarify the broader scope and technical cause.
Until further details are reported, the incident should be treated as a confirmed refrigeration disruption within several Coopérative U stores alongside additional claims about other retailers and store systems. The source material does not provide a timetable for a completed investigation or a statement on when all affected operations would return to normal.
Key Questions
Which supermarket chains are reported to be affected?
The report names Intermarché, Leclerc and Coopérative U as users of the affected Danfoss-made refrigeration controls. The direct confirmation quoted is from Coopérative U; the supplied material does not include statements from the other chains.
What did Coopérative U confirm?
President Dominique Schelcher said refrigeration production facilities in several stores in the network had been affected since the previous night. He said teams were mobilized and an investigation was planned.
Were fridges definitely set to defrost at 50 degrees Celsius?
That setting was reported by Tom’s Hardware citing La Dépêche. It is not included in the quoted confirmation from Schelcher, so the supplied material does not independently establish how many units were affected or whether the setting applied across stores.
Were food supplies or customer data affected?
The available report does not confirm spoiled food, customer data exposure, or any other direct customer harm. It also gives no store count, loss estimate or detailed account of the reported delivery and electronic price-label problems.
Source: hn
Columbus Day / Indigenous Peoples' Day Picks
long weekend sales
As an affiliate, we earn on qualifying purchases.